Complete endpoint coverage for modern organizations
Opsiton combines threat intelligence, AI monitoring and data loss prevention in a native endpoint agent and browser extension, managed from a single security console.
Real-time decisions at the endpoint
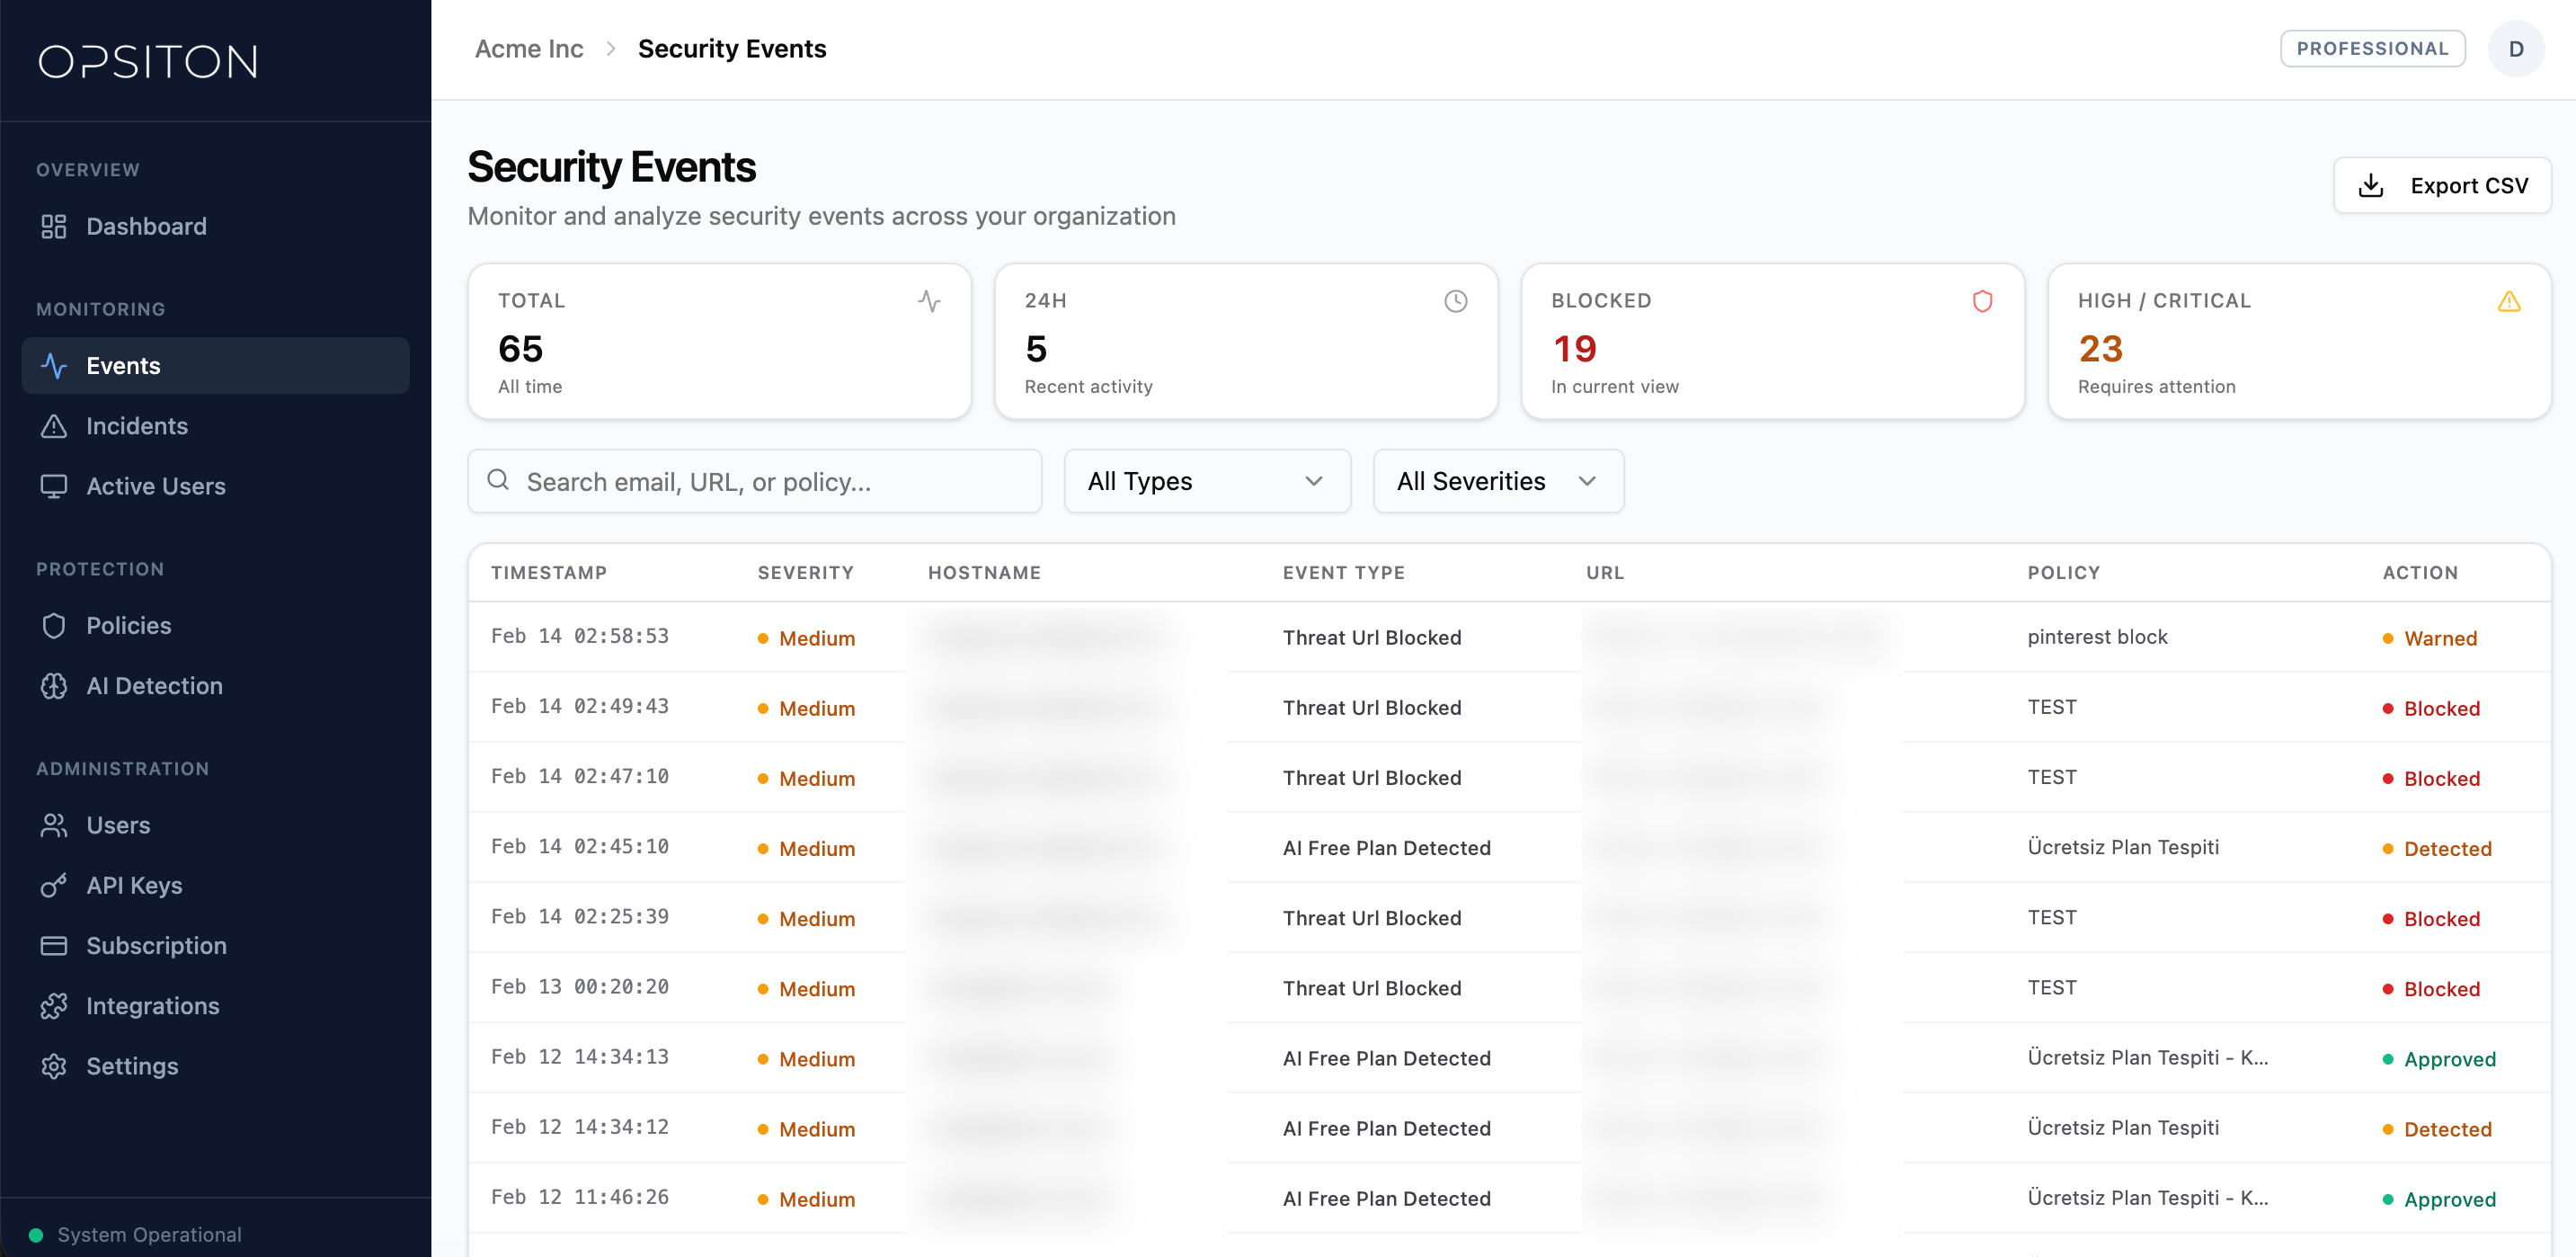
The local agent evaluates every URL, upload and AI prompt against your policies and returns an allow, warn or block decision before the data leaves the device.
Threat URL Detection
Real-time URL scanning with threat intelligence feeds and custom blocklists.
AI Platform Monitoring
Track and control usage of ChatGPT, Claude, Gemini, and other AI tools.
DLP Policy Enforcement
Block sensitive data from leaving your organization through the browser.
Incident Management
Automatic incident creation with email alerts and severity-based escalation.
Built for security teams, loved by IT admins
Every feature is designed with security operations in mind, from policy creation to incident response. Everything works together seamlessly.
Security Analytics
Real-time dashboards with event trends, severity breakdowns, and top websites.
Device Management
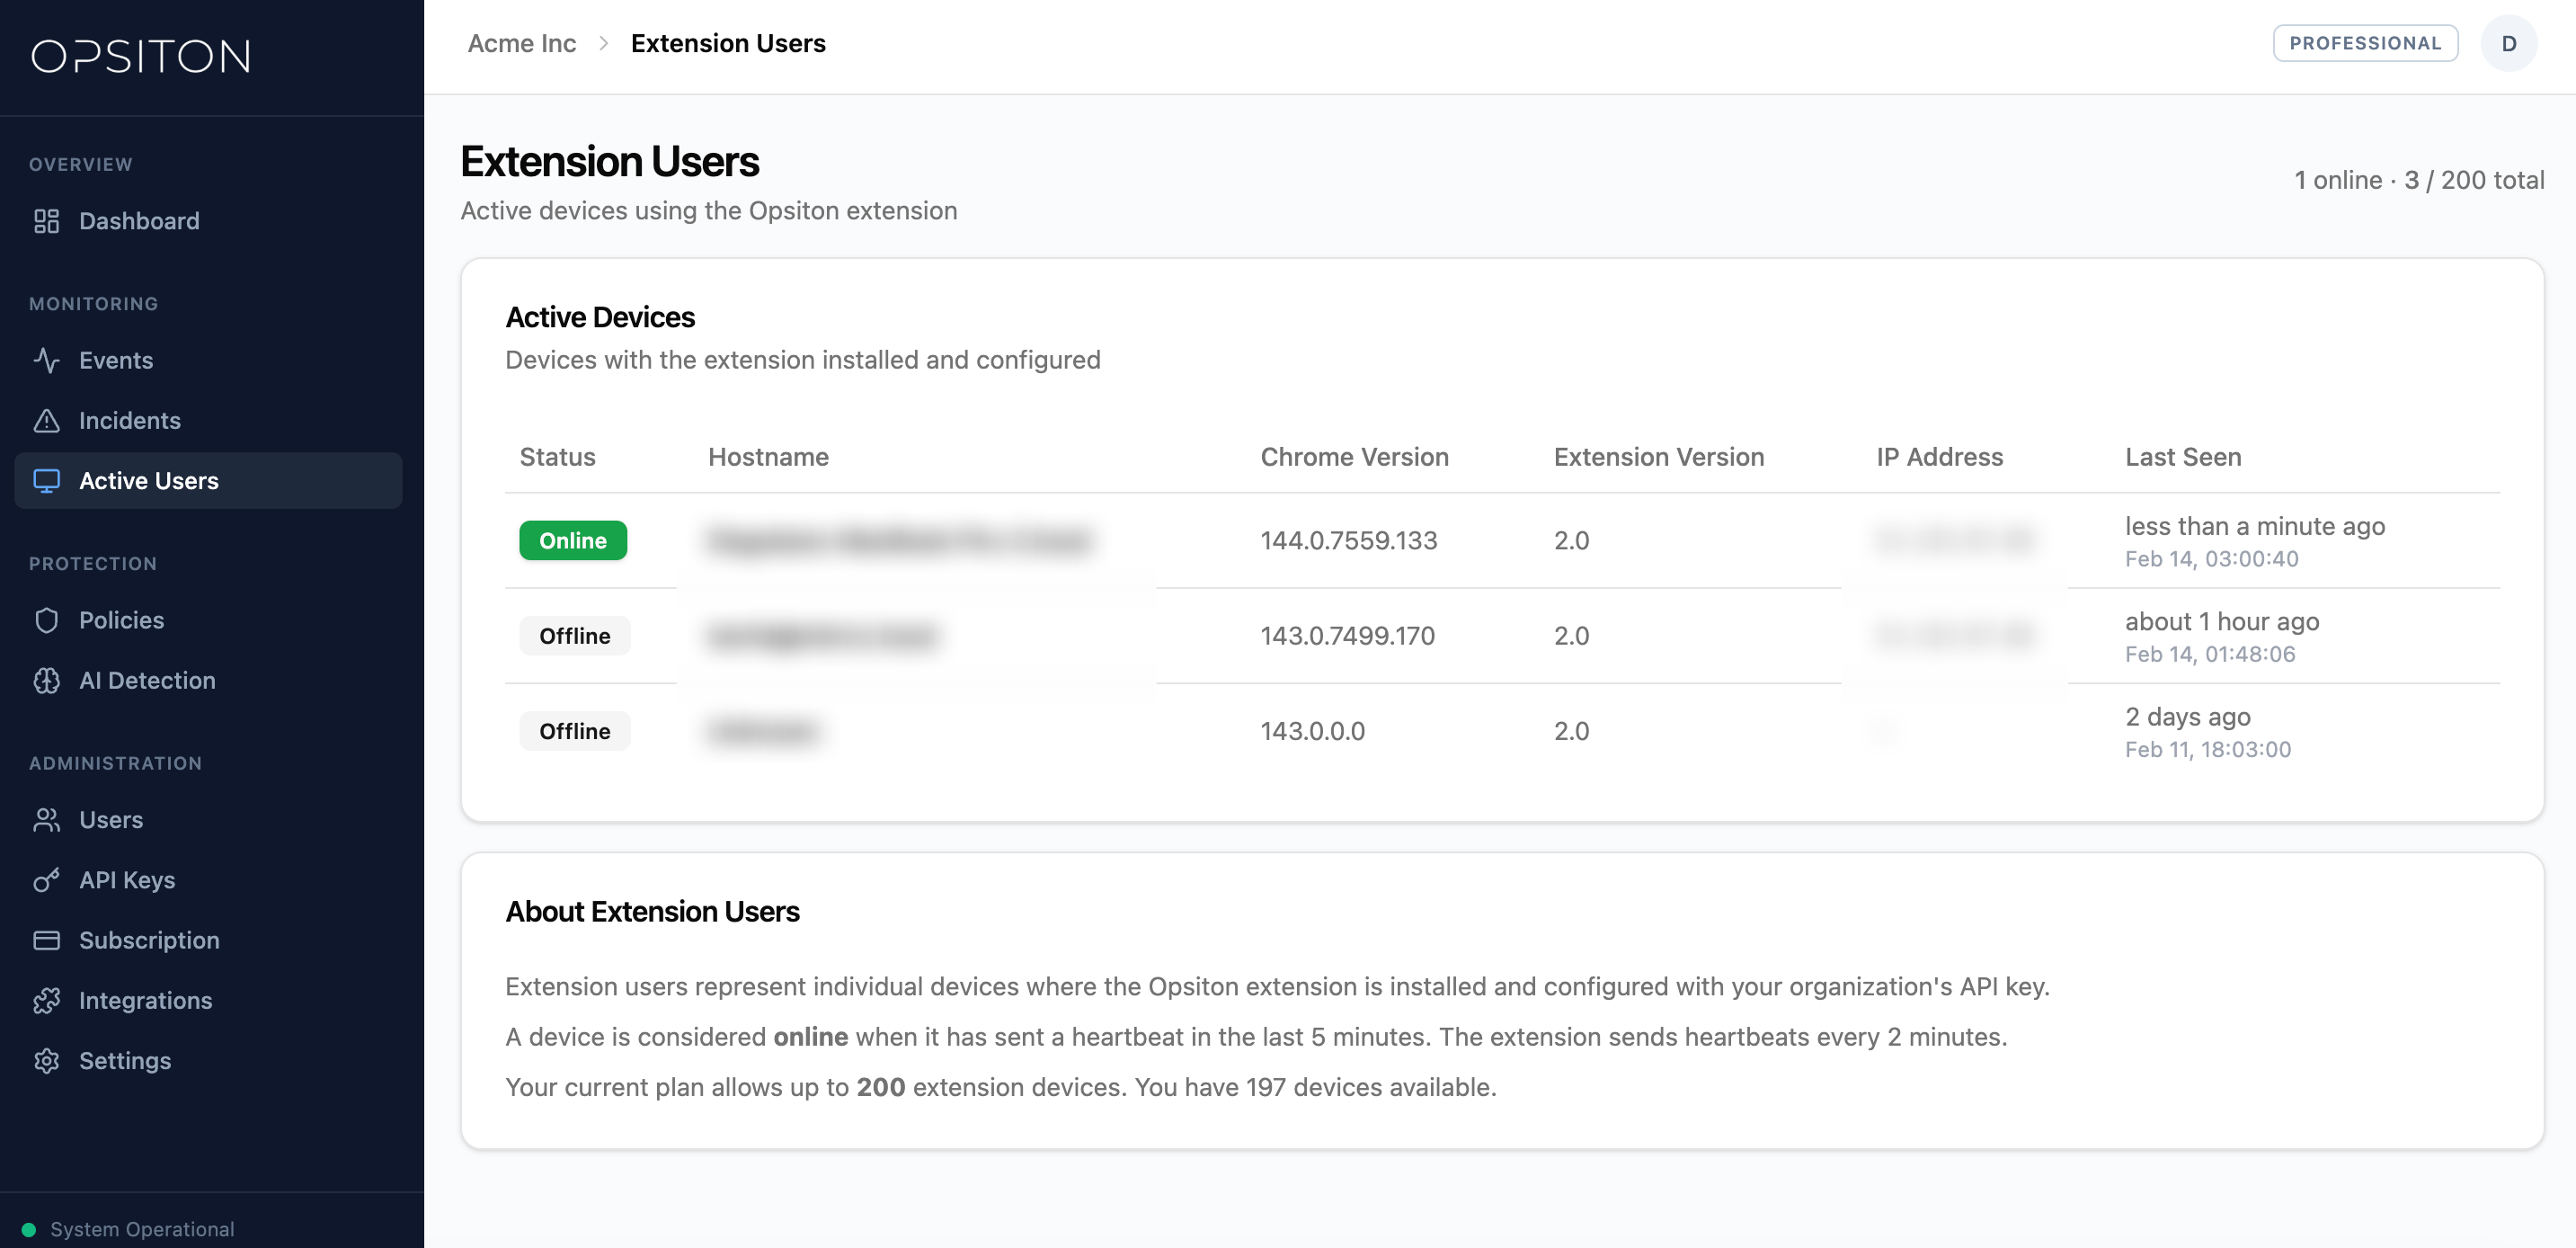
Track all extension endpoints with Chrome version, IP, and heartbeat monitoring.
API-First Architecture
RESTful API with API key authentication for seamless extension deployment.
Multi-Tenant Platform
Isolated organizations with role-based access and subscription management.
From a policy in the portal to a decision on the endpoint
Opsiton connects policy management, local inspection and incident workflows without presenting every surface as the same thing.
Create and publish rules centrally, then target them to host and policy groups.
- Text DLP
- File and file-content DLP
- Threat URL rules
- Block, warn or log actions
The endpoint agent evaluates matching rules and applies the highest-severity decision.
- Regex and GLiNER-based detection
- TCKN, TR IBAN, card and token checks
- PDF and office-document extraction
- Turkish and English OCR for images
The extension currently has explicit adapters for six AI services.
- ChatGPT
- Claude
- Gemini
- Perplexity
- DeepSeek
- Copilot
Security events can feed incident workflows without copying the raw matched value into the event record.
- Masked snippet and content hash
- Sanitized URL without query or fragment
- Critical, high, medium and low severity
- Open, investigating, resolved and closed states